

Healthcare-aware AI architecture is not a feature
If you build for healthcare, data flow, provider routing, and access limits need to reflect those requirements from the start. You cannot bolt them on at the end and expect the system to behave correctly.
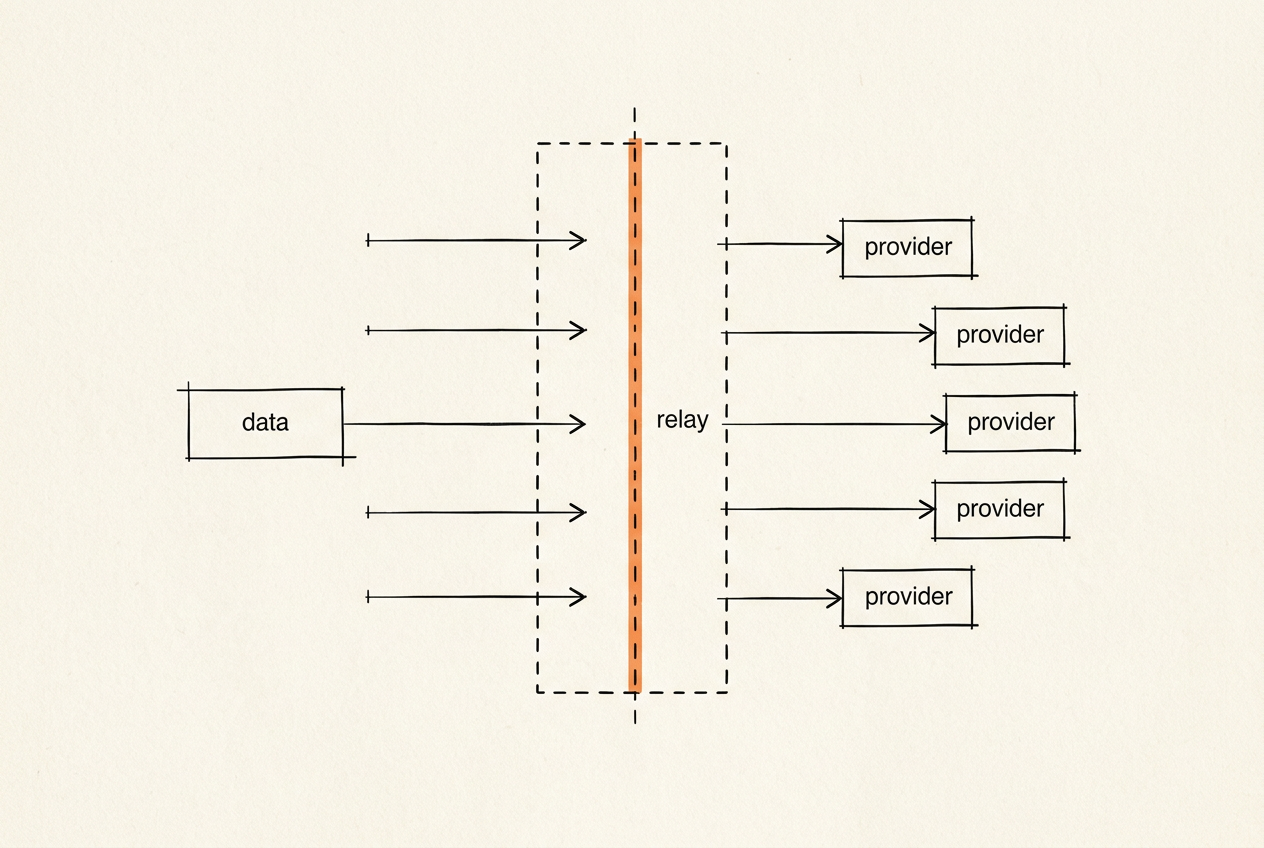
Healthcare-aware AI architecture is not something you add at the end. It shapes the system from the start:
- what data is collected;
- where data is stored;
- which vendors receive data;
- who can access it;
- what is logged;
- what is reviewed by humans;
- how errors are handled;
- what claims the product can safely make.
If a product may touch PHI, PII, clinical workflows, patient communication, or sensitive operational data, architecture decisions are also risk decisions.
Risk Does Not Come Only From the Model
When people discuss AI risk in healthcare, they often focus on the model. That matters, but the surrounding system matters too. Questions to answer:
- Does sensitive input go to an external AI provider?
- Is the provider boundary documented?
- Are access roles defined?
- Is there an audit trail?
- Are outputs reviewed before they affect a person?
- Do logs store sensitive content?
- Can the system explain what happened?
- Are compliance claims scoped carefully?
The model is only one part of the product.
HIPAA-Aligned Does Not Mean Legally Complete
Honest framing
Healthcare-aware architecture can support compliance work. On its own, it does not constitute HIPAA, GDPR, or any other formal compliance certification.
Public wording should stay careful. Technical architecture can support HIPAA-aligned safeguards, NIST-aware practices, auditability, access control, and data minimization. But legal compliance depends on the full context:
- infrastructure;
- vendors;
- contracts;
- operations;
- policies;
- user roles;
- legal review;
- organizational controls.
That is why ITNeuroNet uses precise technical language and does not promise universal compliance.
What Healthcare-Aware Architecture Includes
Depending on the project, this work may include:
- mapping sensitive data flows;
- system boundary model;
- access control model;
- audit trail design;
- encryption assumptions;
- AI provider routing;
- vendor boundary review;
- human review workflow;
- test and security strategy;
- implementation documentation.
Why This Matters Early
Late changes are expensive. If sensitive data has already been routed through the wrong provider, logged in the wrong place, exposed to the wrong role, or mixed with analytics data, the product may need structural changes. Early architecture reduces that risk.
ITNeuroNet's Approach
ITNeuroNet helps design healthcare-adjacent and sensitive-data systems with privacy-first architecture, auditability, and compliance-aware technical planning. The goal is to make implementation safer to review, easier to explain, and better prepared for future legal, operational, or security review.
Discuss a Sensitive-Data Project
If your AI product may touch healthcare, PHI, PII, or sensitive workflows, design the boundary before implementation scales.
More on Healthcare
- Article · Feb 11, 2026
AI agents are becoming a new security boundary
Agents that can call tools and route requests to different providers increase the number of places where a system can be exposed. Security review needs to cover those paths too, not just the API edge.
- Article · Sep 23, 2025
AI governance starts in the product workflow
Policy documents are not enough on their own. Governance has to show up in how features are defined, built, and reviewed before they reach production.