

AI governance starts in the product workflow
Policy documents are not enough on their own. Governance has to show up in how features are defined, built, and reviewed before they reach production.
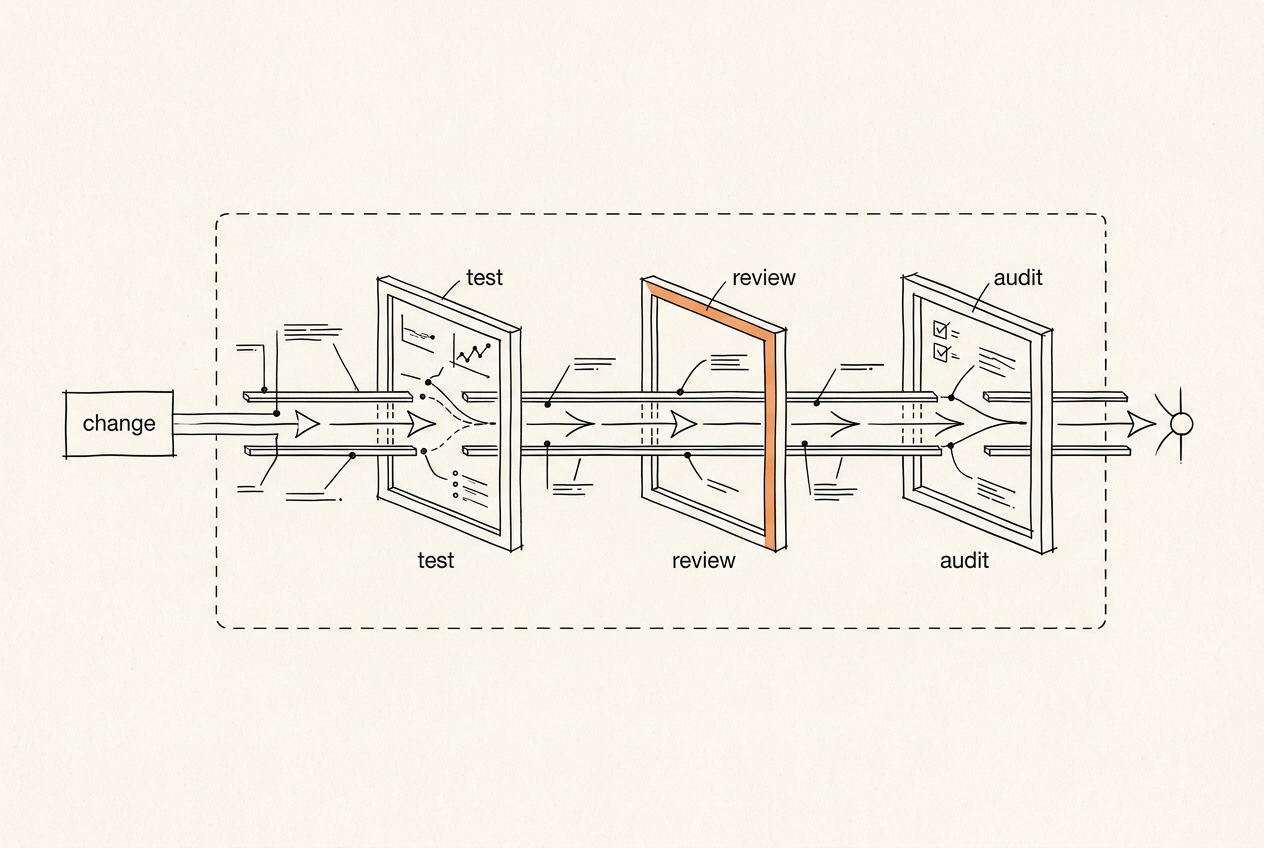
AI governance is often treated as a policy document. Policy matters. But for product teams, governance also needs to show up in system design.
The product needs to decide:
- what data AI can receive;
- what outputs require review;
- what actions are automated;
- what actions are forbidden;
- who can override the system;
- what gets logged;
- what happens when confidence is low;
- how incidents are investigated.
These are not just legal or compliance questions. They also shape the workflow and the system architecture.
Governance Cannot Live Only Outside the Product
If the product workflow lets any user send sensitive data to any provider, policy is not enough. If an agent can call production tools without scoped permissions, policy is not enough. If the system cannot show what happened, policy is not enough.
AI governance needs implementation points:
- permissions;
- data routing;
- model/provider selection;
- logging;
- human review;
- escalation;
- testing;
- monitoring.
Practical Governance Questions
Before you build an AI workflow, ask:
1. What user task is the AI supporting?
2. What data is allowed?
3. Which provider or model receives which data?
4. Which output can be shown directly?
5. Which output needs human review?
6. Which actions can the system take?
7. What needs to be logged?
8. What failure modes exist?
9. Who is responsible for review and correction?
Human Review Should Be Specific
"Human in the loop" is too vague. Better to define it like this:
- summaries can be generated automatically;
- recommendations require user confirmation;
- external messages require approval;
- high-impact actions are blocked;
- workflows involving sensitive data are logged;
- low-confidence output is escalated.
This is how governance becomes part of day-to-day work.
ITNeuroNet's Approach
ITNeuroNet designs AI workflows around product behavior, data boundaries, access control, review loops, and auditability. The aim is to help teams use AI without leaving governance to the end.
Discuss AI Workflow Governance
If your product uses AI in a workflow that touches users, data, tools, or decisions, design the governance into the product from the start.
More on Architecture
- Article · May 14, 2026
Why time-to-market is changing in the AI-native software era
Speed no longer comes from typing code faster. It comes from turning product questions into system changes you have checked, can explain, and can deploy safely.
- Article · Apr 22, 2026
Faster code is not faster delivery
Why faster code generation does not shorten a project by itself, and what else must be in place for AI-supported development to save time instead of creating rework.
- Article · Feb 11, 2026
AI agents are becoming a new security boundary
Agents that can call tools and route requests to different providers increase the number of places where a system can be exposed. Security review needs to cover those paths too, not just the API edge.