

Build carefully when data sensitivity matters
ITNeuroNet designs AI, data, healthcare-adjacent, and other sensitive-data systems with privacy in mind from the start, along with traceable decisions and technical planning that takes compliance requirements into account.
If your product handles healthcare or other sensitive data, you need more than a list of features. Before building, you need to decide what data the system may store, who can access it, where it moves, how actions are logged, what encryption you rely on, which providers are involved, what must be documented, and how the system will be run day to day.
ITNeuroNet supports projects that need safeguards aligned with HIPAA and informed by NIST, where the context calls for them, while avoiding careless public claims about certification or legal compliance.
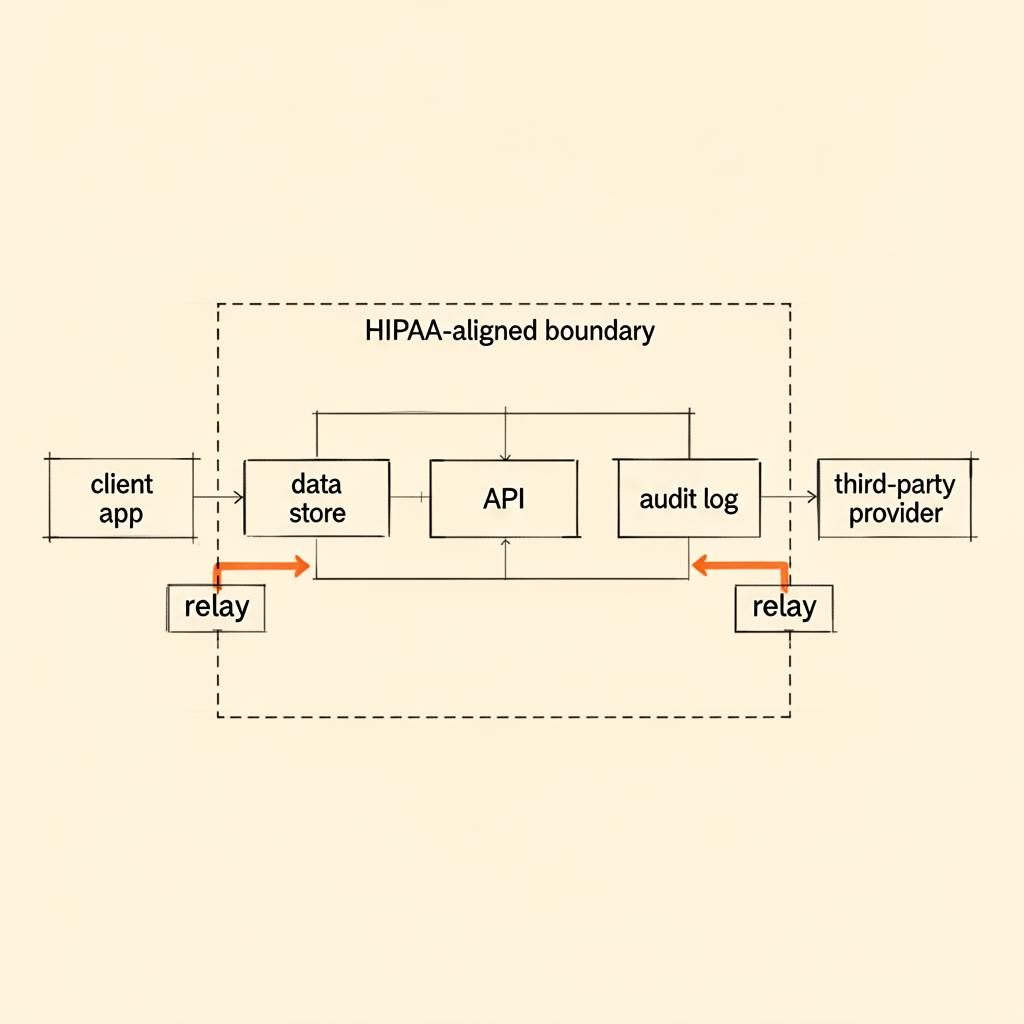
What compliance-aware architecture means in practice
Map sensitive data flows before implementation.
Define system boundaries and provider responsibilities.
Plan access control, roles, audit trails, and encryption assumptions.
Reduce unnecessary data exposure through minimization and isolation.
Design AI-provider routing with privacy and vendor risk in mind.
Document decisions so the system can be reviewed later.
Projects where careful architecture is essential
- Health-tech MVPs and patient-facing products
- Internal healthcare tools and operational systems
- AI workflows that handle sensitive user input
- Speech, transcription, or analytics systems that process personal or business-sensitive data
- Products that may handle PHI, PII, audit logs, or regulated workflows
Where this approach has been applied
Examples of how privacy requirements and data architecture were approached, without revealing confidential implementation details.
Whether a project is compliant depends on the whole setup: infrastructure, vendors, contracts, daily operations, and legal review. ITNeuroNet can help you plan the system and implementation with those requirements in mind, but it does not promise that every project will meet every legal standard in every context.
Planning a healthcare or sensitive-data system?
A good starting point is an assessment of your data flows, system boundaries, architecture risks, and the technical decisions that should be made before anyone starts building.